
Enterprises face high alert volumes and new CVEs. Security teams manage many false positives and large data sets. These conditions cause staff burnout and inefficient operations.
- Security professionals spend more than three hours daily validating false positives. This workload costs organizations up to $500,000 annually.
- 2024 recorded 40,003 new CVEs. This is a 38.83% increase. Teams handle 108 new vulnerabilities daily. Manual processes cannot handle this volume.
- 65% of SOC professionals consider leaving their jobs due to stress and burnout. This loss reduces team stability and weakens security posture.
- Organizations using manual processes face higher breach costs. Teams using AI and automation reduce breach costs by an average of $2.22 million and detect breaches 98 days faster.
These challenges require a shift to intelligent automation.
What Is AIResolveX? Generative AI for Vulnerability Management
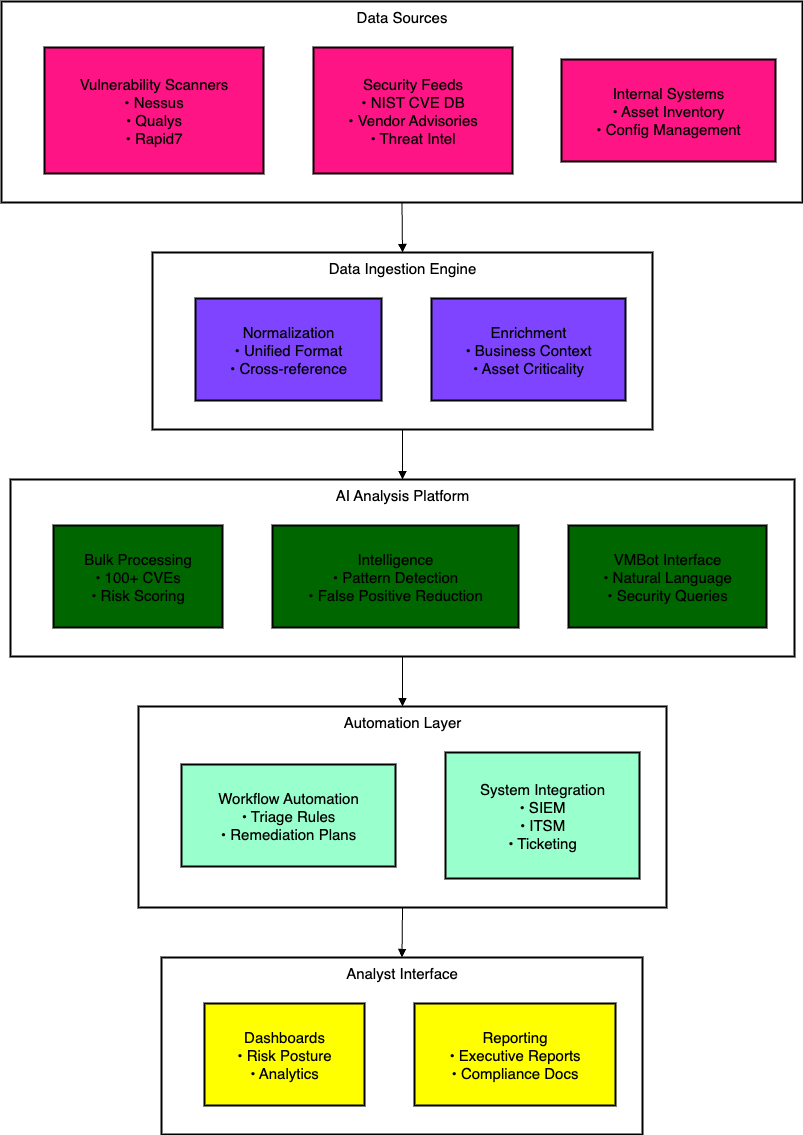
AIResolveX by SquareShift is a generative AI platform that transforms vulnerability management from reactive to proactive. It integrates with Nessus, Qualys, and Rapid7 scanners. It monitors over 100 vendor patch feeds and the global CVE database.
Core Capabilities
- Real-Time Threat Alert: Cross-references published CVEs against asset inventories. Calculates business impact. Generates contextual remediation steps. Alerts relevant analysts.
- Data Correlation: Removes duplicate alerts and false positives across scanning platforms. Achieves 99.98% accuracy. Reduces false positive investigations by 90%.
- VMBot: AI Security Analyst: Uses natural language queries to retrieve vulnerability data. Analysts ask specific questions (e.g., "Is CVE-2024-12345 exploitable in our environment?").
- Bulk Vulnerability Analysis: Analyzes hundreds of CVEs simultaneously. Assigns risk scores based on business impact. Generates tailored remediation plans. Completes tasks three times faster than manual methods.
- Proactive Patch Intelligence: Monitors 100+ vendors. Notifies teams immediately. Assesses patch criticality. Reduces mean time to patch by up to 75%.
Strategic Relevance of AI-Driven Security in Current Enterprise Environments
Current factors drive adoption: rapid CVE growth, security staff shortages, and proven financial returns from automation. AI-driven vulnerability management addresses these pressures.
AIResolveX provides these strategic advantages:
- Risk Management Transformation: Enables proactive risk management. Correlates threats in real time. Prioritizes assets automatically.
- Competitive advantage through speed: Resolve vulnerabilities 98 days faster than competitors. Foster innovation through security confidence.
- Operational excellence: Reallocate resources from false positive validation to strategic initiatives. Save $500,000 annually.
Case Study
Financial Services: Shift From Compliance Burden to Security Leadership
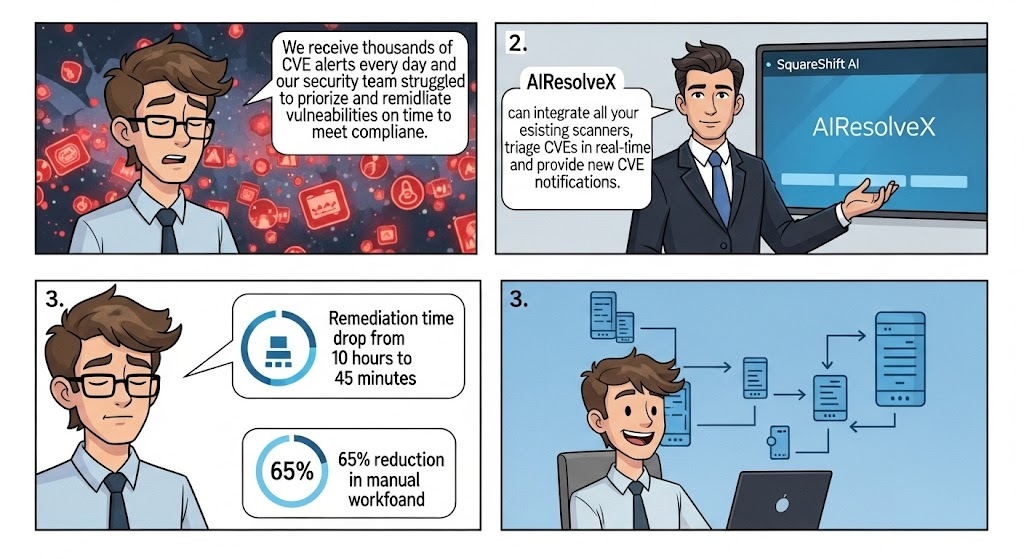
For a worked example, read the case study on unifying five scanning tools into one source, and our guide to cloud security monitoring.
Conclusion: Select a Solution Based on Evidence
Rising vulnerability volumes, workforce fatigue, and automation benefits support immediate adoption.
AIResolveX achieves the following results:
- 75% reduction in manual workload.
- 90% reduction in false-positive investigation time.
- 63x faster CVE analysis.
- Increase in analyst job satisfaction and retention.
Financial Returns
- 650% return on investment (ROI) within three years.
- Removal of up to $500,000 in annual false positive validation costs.
- Payback period of 8 to 12 months.
Strategic Positioning
- Workforce Stability
- Operational resilience during high-risk periods
- Competitive advantage via faster response times
- Infrastructure for future automation
Transform vulnerability management operations now. Contact SquareShift Technologies for a demonstration and ROI assessment.
Contact experts
Sources:
- False Positive Validation Research
Industry cybersecurity workforce studies on false positive burden
Source: Industry security surveys and time-motion studies
URL: https://www.bitsight.com/blog/5-shocking-it-cybersecurity-burnout-statistics
URL: https://www.invicti.com/blog/web-security/false-positives-web-application-security/
- Manual Validation Cost Analysis
Enterprise security operational cost studies
Manual validation of false positives costs up to $500,000 annually per enterprise.
Source: https://www.websecinsights.com/risk-management/eliminating-false-positives-vulnerability-scanning/
Source: https://www.edgescan.com/are-false-positives-really-a-thing-in-2022-for-vulnerability-management-programs/
- 40,003 CVEs published in 2024. A 38.83% increase from 2023.
Source: https://nvd.nist.gov/general/nvd-dashboard
Additional: https://cyberpress.org/over-40000-cves-published-in-2024/
Verification: https://www.cvedetails.com/vulnerability-list/year-2024/vulnerabilities.html
- Ponemon Institute Cybersecurity Burnout Research
65% of SOC professionals consider leaving due to stress
URL: https://www.businesswire.com/news/home/20190729005244/en/Ponemon-Institute-and-Devo-Technology-Study-Reveals-65-of-Cybersecurity-Analysts-Consider-Quitting-Due-to-Burnout-Lack-of-Visibility Additional: https://www.devo.com/company/newsroom/ponemon-institute-and-devo-technology-study-reveals-65-of-cybersecurity-analysts-consider-quitting-due-to-burnout-lack-of-visibility/
- IBM Cost of a Data Breach Report 2024: Automation Savings
AI and automation deliver average savings of $2.22 million
Source: https://www.ibm.com/reports/data-breach
Direct Report: https://www.ibm.com/think/insights/cost-of-data-breaches-business-case-for-security-ai-automation