
Elastic SIEM provides a central view of internal and external environment activity.
- Ingest data from common security tools.
- Use one-click integrations.
- Apply community-built plug-ins.
- Build simple custom connectors.
CrowdStrike is a leading global cybersecurity provider. It offers an advanced cloud-native platform that protects endpoints, cloud workloads, identities, and data.
This article describes how to integrate CrowdStrike Falcon threat detections into Elastic SIEM.
- Utilize Elasticsearch querying and visualization capabilities.
- Establish Elastic SIEM as the central platform.
- Maintain a holistic view of organizational security posture.
In short: the Falcon SIEM Connector writes CrowdStrike threat detections to a log path, Elastic Agent reads them into Elasticsearch, and Elastic SIEM visualises them.
Scope:
- Set up a sandbox environment to generate threats.
- Detect threats using CrowdStrike EDR.
- Configure the Falcon SIEM connector to share alerts.
- Consume alerts via Elastic Agent and visualise them in Elastic SIEM.
System Architecture
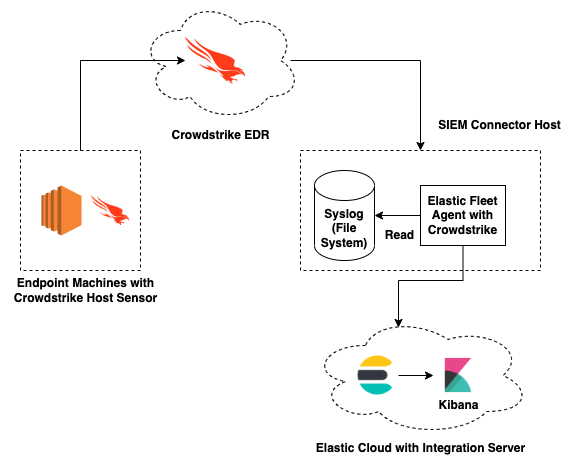
The system comprises three core components:
- Endpoint Machines
- CrowdStrike EDR
- Falcon SIEM Connector
Endpoint Machines:
Machines where the CrowdStrike Host sensor is installed for continuous monitoring of suspicious activities. The Host sensor is a lightweight application that actively scans for threats without manual virus scans.
CrowdStrike EDR:
Falcon Insight™ is the Endpoint Detection and Response (EDR) module of CrowdStrike Falcon® endpoint protection.
This module provides real-time visibility into endpoint security events. It reduces the risk of silent failures that allow intruders to remain undetected.
Falcon SIEM Connector
The SIEM Connector ingests SIEM data streams.
How to Integrate CrowdStrike with Elastic SIEM
Pre-requisites
- CrowdStrike account
- Endpoint machines with CrowdStrike sensor or CrowdStrike Falcon Sandbox installed
- Elastic Cloud with Kibana and Integration Server
- Virtual machine to run the SIEM connector and Fleet Agent with the CrowdStrike agent
Malicious Activities
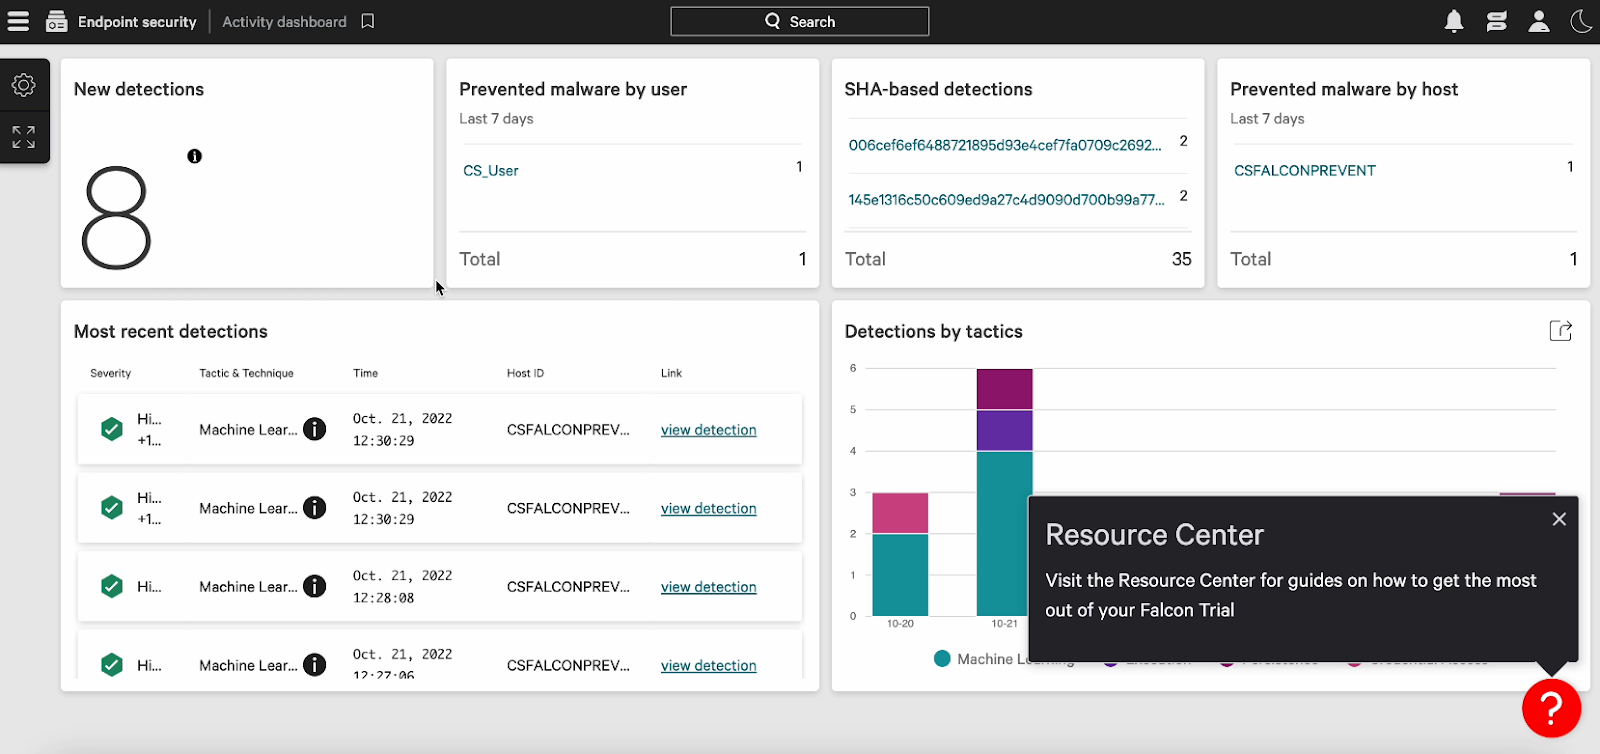
After completing prerequisites, execute malware payloads on endpoint machines that have the CrowdStrike host sensor.
CrowdStrike EDR displays detected threats and related details in the Endpoint Security Dashboard.
Elasticsearch Visualization
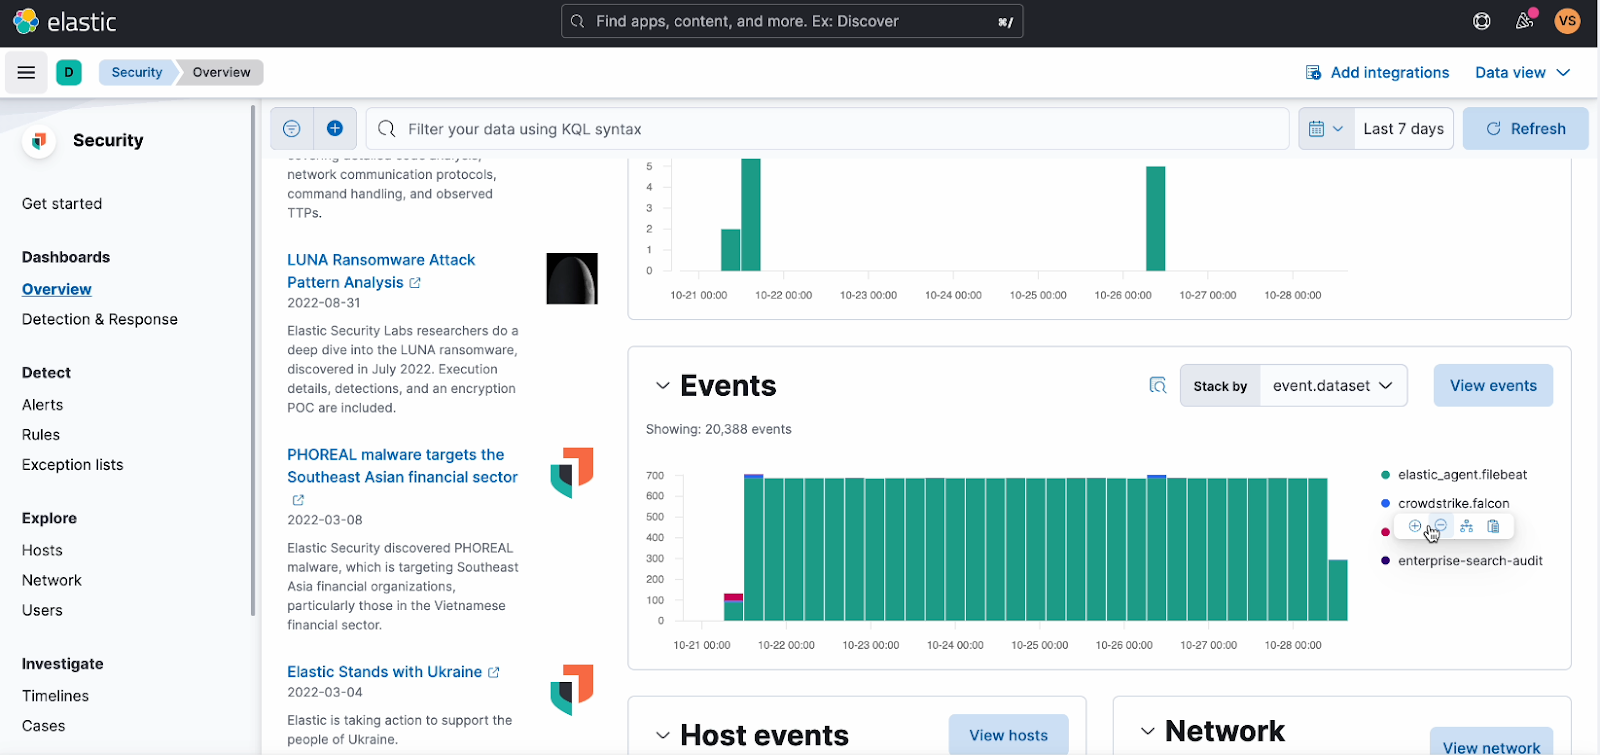
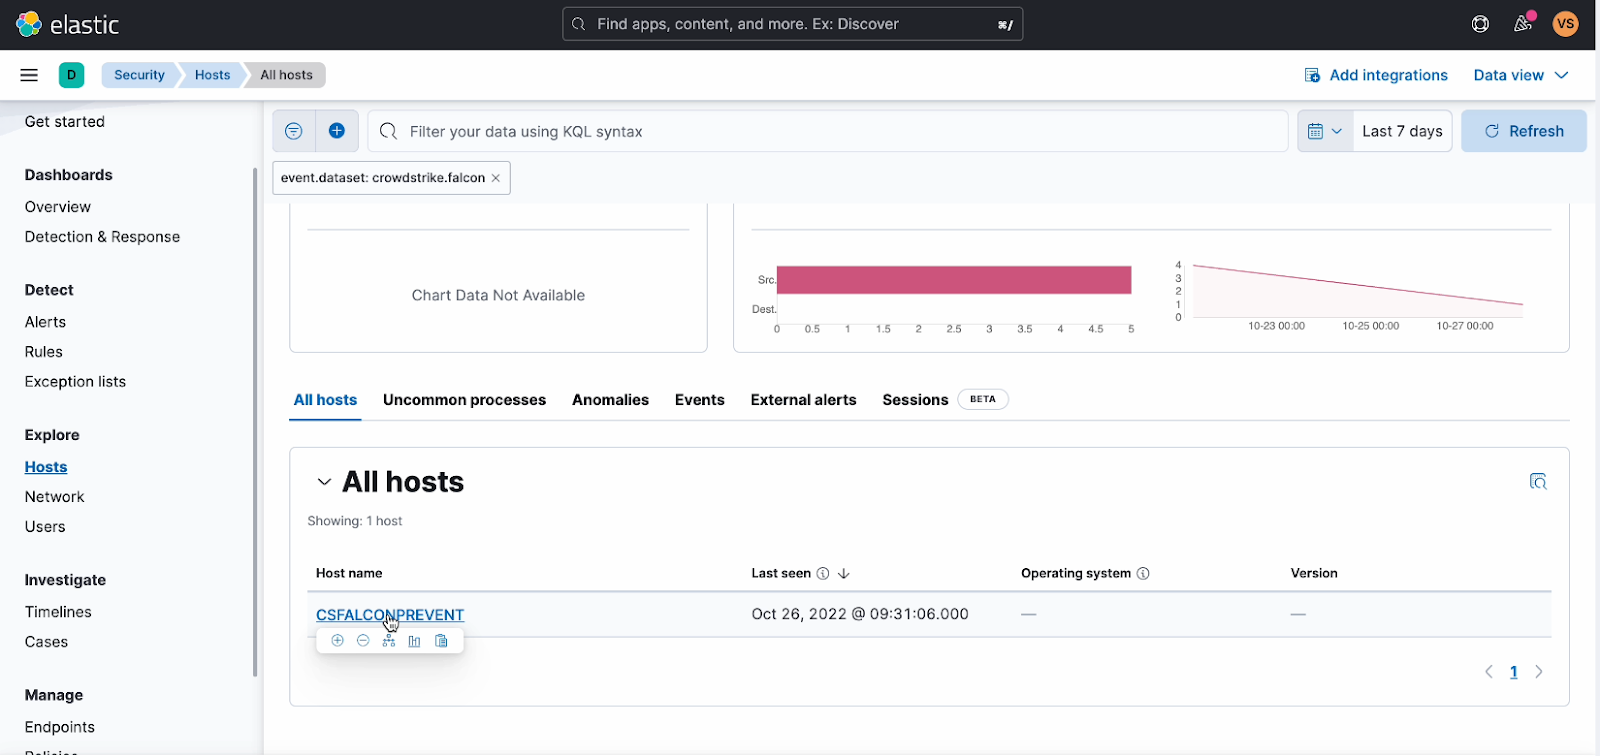
The SIEM Connector polls threats and writes them to /var/log/crowdstrike/falconhoseclient/output by default. The Elastic Agent reads from this path and pushes data to Elasticsearch. The Elastic Agent maintains ECS format compliance.
Conclusion
Elasticsearch provides strong querying and aggregation capabilities. Kibana uses these aggregations to define custom visualization dimensions that CrowdStrike does not provide.
For help running Elastic security monitoring, see our Elastic services for security monitoring.
Related reading: Elastic vs Splunk for security analytics and observability and what Elastic Observability covers.
Sources:
- https://www.crowdstrike.com/blog/tech-center/integrate-with-your-siem/
- https://www.elastic.co/guide/en/beats/filebeat/current/filebeat-module-crowdstrike.html
- https://www.crowdstrike.com/products/threat-intelligence/falcon-sandbox-malware-analysis/